AI Cyber Security Intelligence
for the New Era
of Digital Threats
Encrygma helps enterprises, executives, governments, financial institutions, law firms, and critical infrastructure operators monitor, understand, and respond to AI-driven cyber threats, ransomware, spyware, deepfakes, state-sponsored attacks, zero-day risks, and emerging cyber intelligence signals.
AI-Enhanced Phishing Campaigns
Global
State-Sponsored APT Activity
Asia-Pacific
Mercenary Spyware Deployments
Middle East
Ransomware Escalation Trends
Europe
Zero-Day Exposure Alerts
N. America
Encrygma Intelligence Brief: The Escalation of AI-Driven Cyber Operations and Ransomware Velocity
Encrygma analysts report a surge in AI-integrated malware frameworks and persistent ransomware activity. We assess the current threat landscape as a critical inflection point for defensive strategy.
Encrygma Daily Brief: The Rise of Agentic AI Exploitation and Ransomware Persistence
Encrygma analysts assess a critical shift toward agentic AI in cyber operations, evidenced by the deployment of frameworks like ARTEX. We evaluate the current ransomware surge and defensive strategies.
Encrygma Daily Brief: The AI-Driven Acceleration of Exploitation and Ransomware Persistence
Encrygma threat data confirms a surge in AI-assisted malware development and critical infrastructure targeting. We analyze the shift toward automated vulnerability exploitation and its impact on security.
Encrygma Brief: The Rise of Agentic AI Exploitation and the 'Black October' Cyber Crisis
Encrygma analysts assess that the rapid adoption of agentic AI frameworks like ARTEX and VoidLink has fundamentally shifted the threat landscape, enabling autonomous, multi-stage cyber campaigns.
Encrygma Brief: The Rise of Agentic AI Exploitation and the PHP Critical Vulnerability Crisis
Encrygma analysts track a surge in agentic AI-driven post-exploitation and the global fallout from critical PHP vulnerabilities. We assess the shifting landscape of autonomous cyber threats.
Encrygma Brief: The Rise of Autonomous AI Agents and Machine-Speed Cyber Campaigns
Encrygma threat data confirms a surge in autonomous AI-driven cyber campaigns, with state-aligned actors now executing attacks at machine speed. We analyze the shift toward agentic threat vectors.
Encrygma Brief: The Weaponization of Agentic AI and the 'Black October' Surge
Encrygma analysts assess a critical shift in threat actor methodology as state-aligned groups weaponize agentic AI frameworks. This surge, dubbed 'Black October,' demands a recalibration of defensive posture.
The AI Acceleration: Analyzing the 'Black October' Cyber Threat Landscape
Encrygma analysts assess that the rapid integration of agentic AI into offensive operations has triggered a 'Black October,' marking a critical shift in the speed and scale of automated cyber threats.
Encrygma Intelligence Brief: The Escalation of AI-Driven Cyber Operations and Ransomware Velocity
Encrygma analysts report a surge in AI-integrated malware frameworks and persistent ransomware activity. We assess the current threat landscape as a critical inflection point for defensive strategy.
Encrygma Daily Brief: The Rise of Agentic AI Exploitation and Ransomware Persistence
Encrygma analysts assess a critical shift toward agentic AI in cyber operations, evidenced by the deployment of frameworks like ARTEX. We evaluate the current ransomware surge and defensive strategies.
Encrygma Daily Brief: The AI-Driven Acceleration of Exploitation and Ransomware Persistence
Encrygma threat data confirms a surge in AI-assisted malware development and critical infrastructure targeting. We analyze the shift toward automated vulnerability exploitation and its impact on security.
Encrygma Brief: The Rise of Agentic AI Exploitation and the 'Black October' Cyber Crisis
Encrygma analysts assess that the rapid adoption of agentic AI frameworks like ARTEX and VoidLink has fundamentally shifted the threat landscape, enabling autonomous, multi-stage cyber campaigns.
Encrygma Brief: The Rise of Agentic AI Exploitation and the PHP Critical Vulnerability Crisis
Encrygma analysts track a surge in agentic AI-driven post-exploitation and the global fallout from critical PHP vulnerabilities. We assess the shifting landscape of autonomous cyber threats.
Encrygma Brief: The Rise of Autonomous AI Agents and Machine-Speed Cyber Campaigns
Encrygma threat data confirms a surge in autonomous AI-driven cyber campaigns, with state-aligned actors now executing attacks at machine speed. We analyze the shift toward agentic threat vectors.
Encrygma Brief: The Weaponization of Agentic AI and the 'Black October' Surge
Encrygma analysts assess a critical shift in threat actor methodology as state-aligned groups weaponize agentic AI frameworks. This surge, dubbed 'Black October,' demands a recalibration of defensive posture.
The AI Acceleration: Analyzing the 'Black October' Cyber Threat Landscape
Encrygma analysts assess that the rapid integration of agentic AI into offensive operations has triggered a 'Black October,' marking a critical shift in the speed and scale of automated cyber threats.
Critical PHP2Shell Vulnerabilities Trigger Global Patching Sprint Amidst Widespread Exploitation
Encrygma analysts confirm the active exploitation of the PHP2Shell vulnerabilities (CVE-2026-109618/109619), impacting 70% of the web. Organizations are urged to patch immediately to prevent RCE.
Encrygma Alert: Rise of Agentic AI Exploitation in PHP2Shell Attacks
Encrygma analysts have confirmed a surge in autonomous AI-driven post-exploitation activity targeting government entities. Threat actors are leveraging agentic frameworks to weaponize PHP2Shell vulnerabilities.
Global Infrastructure Under Siege: PHP2Shell and Arista VCO Zero-Days Dominate Threat Landscape
Encrygma analysts report a surge in critical zero-day exploitation targeting PHP environments and Arista networking gear. These flaws enable unauthenticated remote code execution on a massive scale.
Global Government Entities Targeted by AI-Enhanced PHP2Shell Exploitation Campaigns
Encrygma analysts have identified a surge in cyber espionage operations leveraging agentic AI to automate post-exploitation tasks following the abuse of critical PHP2Shell vulnerabilities.
Autonomous AI Agents Weaponize PHP2Shell Vulnerabilities in Global Government Infrastructure Attacks
Encrygma threat intelligence confirms a surge in autonomous AI-driven post-exploitation campaigns targeting government entities. Attackers are leveraging agentic frameworks to weaponize PHP2Shell flaws.
SafePay Ransomware Campaign Escalates Targeting of Global Critical Infrastructure Networks
Encrygma threat data confirms the SafePay ransomware group has compromised over 600 critical infrastructure organizations since August 2024. Analysts warn of a persistent credential-harvesting campaign.
Iranian APT 'Prince of Persia' Deploys US-Based C2 Infrastructure for Global Surveillance Operations
Encrygma analysts have identified a new campaign by the Iranian-linked 'Prince of Persia' group utilizing US-based command-and-control servers. The operation employs sophisticated malware to conduct full-spectrum surveillance on high-value targets.
Global Intelligence Alert: Integrity Technology Group Exposed as Front for Chinese State-Sponsored Cyber Operations
Encrygma analysts have confirmed that Integrity Technology Group serves as a primary infrastructure provider for Chinese APTs. This operation facilitates large-scale espionage against Western targets.
Qilin Ransomware Surge: Global Financial and Legal Sectors Targeted in October 2026 Offensive
Encrygma threat data confirms a massive spike in Qilin ransomware activity, with multiple high-profile victims in the US and Europe reported within the last 48 hours. The group remains a top-tier threat.
Qilin Ransomware Escalates Financial Sector Targeting; N0n Group Dominates October 2026 Threat Landscape
Encrygma threat intelligence confirms a surge in ransomware activity, with the Qilin group targeting Commonwealth Community Bank and the N0n collective aggressively expanding its victim count.
AdFection Campaign: Israeli AdTech Firm Discover-Tech Exposed for Delivering Zero-Click Mercenary Spyware
Encrygma analysts have confirmed that Discover-Tech utilized its 'Controlium' platform to weaponize global ad exchanges, enabling zero-click spyware infections via targeted online advertisements.
Autonomous AI Agents Weaponized in Global Cyber Campaigns: Encrygma Threat Intelligence Update
Encrygma analysts have identified a surge in autonomous AI agents being deployed for post-exploitation and supply chain infiltration. These tools are bypassing traditional security guardrails at scale.
SafePay Ransomware Escalates Global Campaign Targeting 600+ Critical Infrastructure Entities
Encrygma threat intelligence confirms a surge in SafePay ransomware activity, with over 600 critical infrastructure organizations compromised globally. The group is actively exploiting identity vulnerabilities.
Discover-Tech Ad-Injection Pipeline: First Confirmed Zero-Click Mercenary Spyware Delivery via Online Ads
Encrygma analysts have confirmed the discovery of a sophisticated spyware delivery mechanism utilizing the global ad-tech ecosystem. The platform, Controlium, enables zero-click infections via targeted ads.
Critical Infrastructure Alert: Rising OT Vulnerabilities and AI-Driven Threat Vectors in Global Power Grids
Encrygma threat data confirms a surge in OT-targeted cyber activity, with small utilities facing heightened risks from AI-assisted exploits. New federal mandates are being urged to secure grid systems.
Critical Brotli Decoder Vulnerability CVE-2026-111497 Triggers Global Patching Urgency
Encrygma analysts have identified a critical memory corruption vulnerability in the Brotli compression library. Active exploitation risks exist across Node.js, Bun, and various proxy deployments.
Iranian 'Prince of Persia' APT Exploits US-Based Infrastructure for Global Espionage Operations
Encrygma analysts have identified a sophisticated Iranian threat actor, 'Prince of Persia,' utilizing US-based command-and-control servers to conduct long-term surveillance. This campaign targets critical public and private sector entities across the US, Europe, and the Middle East.
Global Ransomware Surge: 47 Organizations Targeted in 24 Hours as SafePay Threat Escalates
Encrygma threat data confirms 47 organizations were listed on ransomware leak sites in the last 24 hours. This follows a major CISA advisory regarding the SafePay group's impact on critical infrastructure.
Panzer Ransomware Group Targets Family Planning Association of Pakistan in Latest Global Campaign
Encrygma analysts have confirmed a significant data breach involving the Family Planning Association of Pakistan, attributed to the emerging Panzer ransomware group. This incident highlights a surge in targeted attacks against non-profit and healthcare-adjacent entities throughout October 2026.
AdFection: Mercenary Spyware Pipeline Exploits Global Ad Exchanges for Zero-Click Mobile Surveillance
Encrygma threat data confirms the emergence of 'AdFection,' a sophisticated pipeline leveraging programmatic advertising to deliver zero-click mercenary spyware to high-value targets globally.
AdFection Pipeline: Mercenary Spyware Exploits Global Ad Exchanges for Zero-Click Mobile Surveillance
Encrygma threat data confirms the emergence of 'AdFection,' a sophisticated pipeline turning programmatic advertising into a delivery mechanism for zero-click mercenary spyware against high-value targets.
Critical Infrastructure Alert: Escalating OT Vulnerabilities and AI-Driven Threats Target Global Utility Networks
Encrygma intelligence confirms a surge in OT-specific vulnerabilities and AI-assisted reconnaissance targeting critical infrastructure. Recent CISA advisories highlight systemic risks to energy and water sectors.
Urgent Security Alert: Active Exploitation of PHP2Shell Vulnerabilities CVE-2026-109618 and CVE-2026-109619
Encrygma analysts have confirmed active in-the-wild exploitation of critical PHP vulnerabilities. Organizations are urged to patch immediately to prevent remote code execution.
October 2026 Threat Landscape: Surge in Zero-Day Exploitation Across Enterprise Infrastructure
Encrygma analysts report a critical spike in zero-day activity targeting Citrix, Cisco, and Windows environments. Organizations are urged to prioritize patching as multiple CVEs enter the CISA KEV catalog.
Encrygma Intelligence Alert: APT28 Escalates Espionage Against NATO Defense Infrastructure
Encrygma analysts have confirmed a surge in cyber espionage by the Russian-linked actor APT28, targeting NATO-aligned naval and aerospace manufacturers. This campaign utilizes sophisticated persistence techniques to exfiltrate sensitive military-industrial data.
AI-Powered 'Black October': PHP2Shell Exploits and Autonomous Agent Campaigns Surge
Encrygma threat intelligence confirms a massive spike in autonomous cyber attacks leveraging AI agents and critical PHP vulnerabilities. These campaigns are rapidly compromising enterprise infrastructure.
Storm-0940 Leverages Agentic AI Framework 'ARTEX' in ConnectWise Supply Chain Compromise
Encrygma threat intelligence confirms China-aligned actor Storm-0940 utilized the ARTEX agentic AI framework to facilitate a supply chain attack on ConnectWise Cloud Backup, marking a shift in AI-driven exploitation.
Nation-State Actors Deploy 'ARTEX' AI Campaign to Compromise Global Software Supply Chains
Encrygma analysts have confirmed a sophisticated, AI-driven cyber campaign designated ARTEX, which is actively targeting critical infrastructure through automated supply chain code injection.
SilentRansomGroup and Qilin Intensify Global Ransomware Campaigns as October Victim Counts Surge
Encrygma threat data confirms a sharp rise in ransomware activity, with SilentRansomGroup and Qilin leading a wave of double-extortion attacks targeting US and international enterprises.
Global Ransomware Surge: Qilin and Whitearmor Lead October 2026 Wave of Extortion Attacks
Encrygma threat data confirms a significant spike in ransomware activity, with Qilin and Whitearmor targeting critical infrastructure. Over 50 organizations were listed on leak sites in the last 24 hours.
AI Summary
What Is AI Cyber Security?
AI cyber security is the intersection of artificial intelligence and cybersecurity — both using AI to defend against threats, and understanding how adversaries deploy AI to attack. As AI becomes embedded in enterprise operations, it simultaneously transforms how threat actors operate.
AI-powered cyber threats include AI-generated phishing at scale, voice and video deepfakes for executive impersonation, automated vulnerability scanning, AI-assisted malware development, and AI-driven disinformation campaigns. Organizations that do not have continuous intelligence on these threats are operating blind in a rapidly evolving threat landscape.
Read: AI Cyber Security Intelligence PlatformAI cyber security is now a board-level risk.
AI attackers scale phishing, reconnaissance, and impersonation faster than humans can detect.
Enterprises need continuous intelligence, not only reactive incident response.
Encrygma focuses on lawful, defensive cyber intelligence.
Platform Coverage
Encrygma Intelligence Focus Areas
Comprehensive AI cyber security intelligence across the full spectrum of digital threats facing enterprises, executives, governments, and critical infrastructure operators.
AI Threat Intelligence
Continuous monitoring of AI-driven attack campaigns, threat actor AI adoption, and emerging techniques.
AI Phishing & Deepfake Defense
Intelligence on AI-generated phishing, voice cloning, video deepfakes, and executive impersonation fraud.
Ransomware Intelligence
AI-enhanced ransomware trends, group activity, industry targeting, and extortion intelligence.
Mercenary Spyware Intelligence
Defensive awareness of commercial spyware, mobile surveillance, and executive device risk.
State-Sponsored Cyber Attacks
Nation-state APT activity, geopolitical cyber risk, and strategic espionage intelligence.
Zero-Day Intelligence
Zero-day exposure awareness, patch intelligence, and exploit risk prioritization.
Critical Infrastructure
Sector-specific intelligence for energy, water, healthcare, telecom, and transportation.
Executive Cyber Risk
Targeted intelligence for CEOs, boards, investors, and high-profile individuals.
Cyber Intelligence Reports
Board-level reports on ransomware, spyware, state operations, zero-day, and sector risk.
Trusted by Practitioners
What Cyber Intelligence Analysts Say
Quotes from anonymous analysts, defenders, and operators who rely on Encrygma intelligence and our promoted security tools in daily operations. Identifying details withheld to protect operational security.
"Encrygma's continuous intelligence feeds have become a backbone of our defensive posture. The depth of attribution analysis on state-sponsored campaigns is rare in this industry."
Senior Threat Intelligence Analyst
Global Financial Institution
"The ransomware and mercenary spyware coverage is unmatched. We shifted from reactive incident response to proactive risk reduction within a single quarter of adopting the platform."
Director of Cyber Defense
Fortune 100 Enterprise
"Their AI phishing and deepfake threat research gave our board the language and evidence needed to fund a serious defensive program. It translated technical risk into executive action."
CISO
International Law Firm
"As a government-affiliated operator, I value intelligence that is verified, attribution-rich, and operationally relevant. Encrygma consistently delivers on all three."
Intelligence Liaison
National Cyber Agency
"The zero-day and critical infrastructure reporting is the most actionable open-source intelligence I consume weekly. It informs patch prioritization across our entire OT estate."
Head of OT Security
Energy Sector Operator
"Executive cyber risk briefings from Encrygma are concise, evidence-backed, and free of vendor hype. Exactly what a board needs to make decisions under uncertainty."
Chief Risk Officer
Family Office
"Within 90 days of feeding Encrygma's ransomware intelligence into our patch prioritization, we cut mean-time-to-patch on critical CVEs by roughly 40% and reduced unresolved dwell-time alerts by a third."
SOC Lead
Global Manufacturer
"The AI-phishing and deepfake briefings let us preempt a targeted executive-impersonation attempt before it reached wire-transfer approval. A single prevented incident paid for the intelligence program many times over."
Head of Third-Party Risk
Asset Management Firm
"Quarterly attribution briefings shifted our cyber-insurance renewal conversation. Underwriters credited our intelligence-led posture with a measurable premium reduction — the ROI was tangible."
CISO
Regional Bank
Identifying information withheld to preserve operational security of contributing analysts.
Latest AI Attack Intelligence
Cyber Technologies
Professional Surveillance & Intelligence Tools
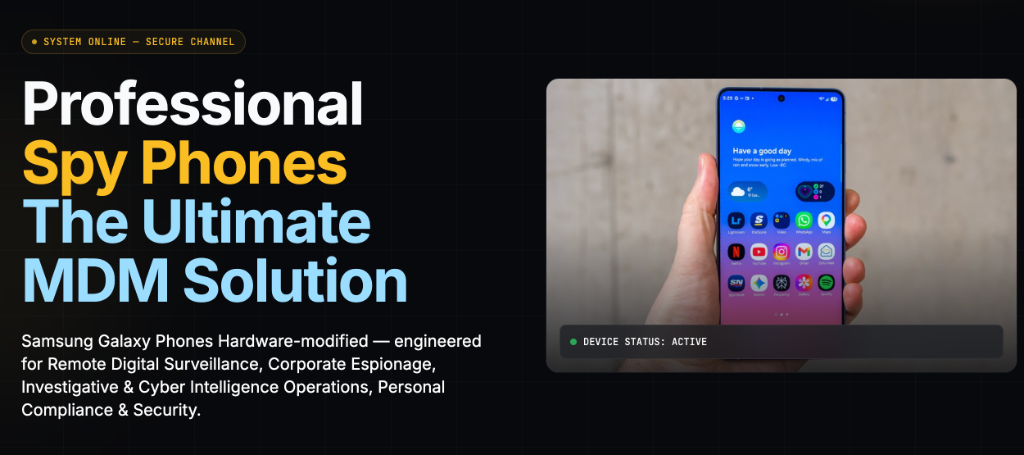
Samsung Galaxy Phones Hardware-modified — engineered for Remote Digital Surveillance, Corporate Espionage, Investigative & Cyber Intelligence Operations, Personal Compliance & Security.
VISIT SPYPHONE.SHOP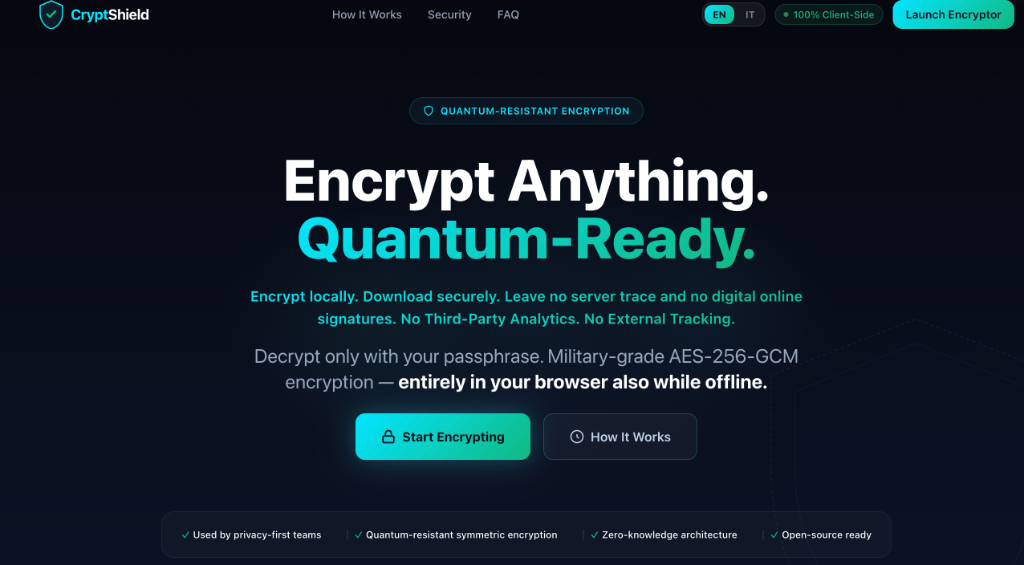
Encrypt Anything.
Quantum-Ready.
Encrypt locally. Download securely. Leave no server trace and no digital online signatures. No Third-Party Analytics. No External Tracking.
Decrypt only with your passphrase. Military-grade AES-256-GCM encryption — entirely in your browser also while offline.
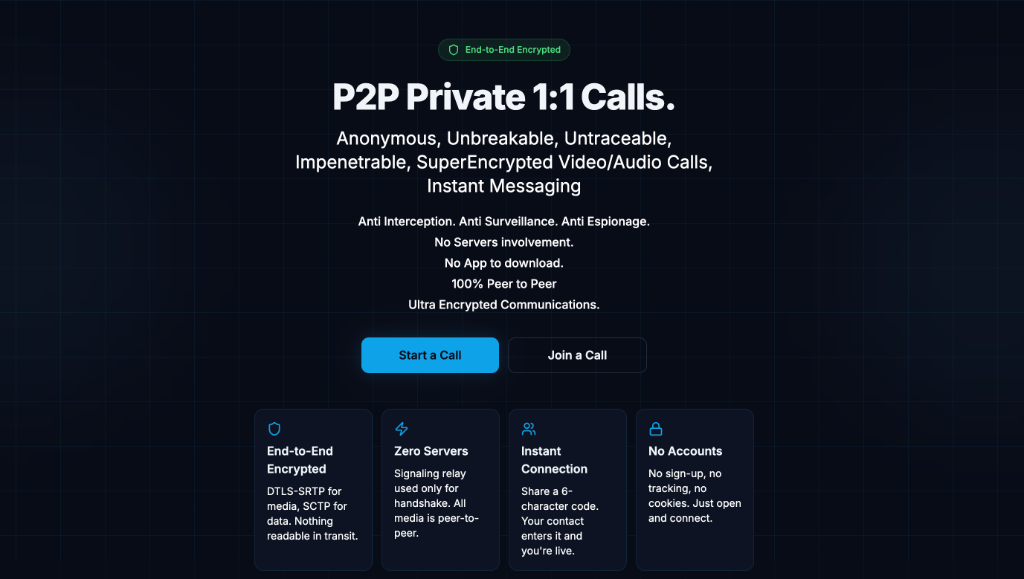
P2P Private 1:1 Calls.
Anonymous, Unbreakable, Untraceable, Impenetrable, SuperEncrypted Video/Audio Calls, Instant Messaging
Anti Interception. Anti Surveillance. Anti Espionage.
No Servers involvement.
No App to download.
100% Peer to Peer
Ultra Encrypted Communications.
Capabilities built for serious security work:
From vulnerability discovery to validated exploits — an autonomous engine that thinks like an attacker and remediates like a defender.
Multi-Agent AI Discovery:
Parallel autonomous agents analyze files simultaneously, ranked by vulnerability likelihood.
Exploit Chain Construction:
Automatically builds full attack chains with PoC payloads and step-by-step exploitation guides.
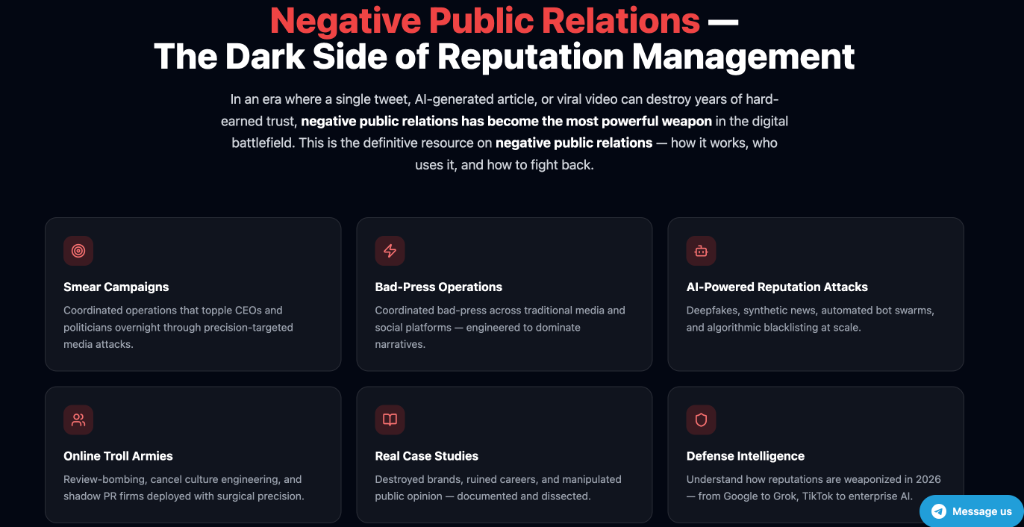
The Dark Side of Reputation Management:
In an era where a single tweet, AI-generated article, or viral video can destroy years of hard-earned trust, negative public relations has become the most powerful weapon in the digital battlefield.
Smear Campaigns:
Coordinated operations that topple CEOs and politicians overnight through precision-targeted media attacks.
Bad-Press Operations:
Coordinated bad-press across traditional media and social platforms — engineered to dominate narratives.
AI-Powered Reputation Attacks:
Deepfakes, synthetic news, automated bot swarms, and algorithmic blacklisting at scale.
Online Troll Armies:
Review-bombing, cancel culture engineering, and shadow PR firms deployed with surgical precision.
CULTIVATING SOVEREIGN OFFENSIVE CYBER CAPABILITIES:
True digital sovereignty is not purchased; it is engineered:
By internalizing the cyber-offensive lifecycle, an agency evolves from a mere consumer of technology to a dominant force in the digital domain.
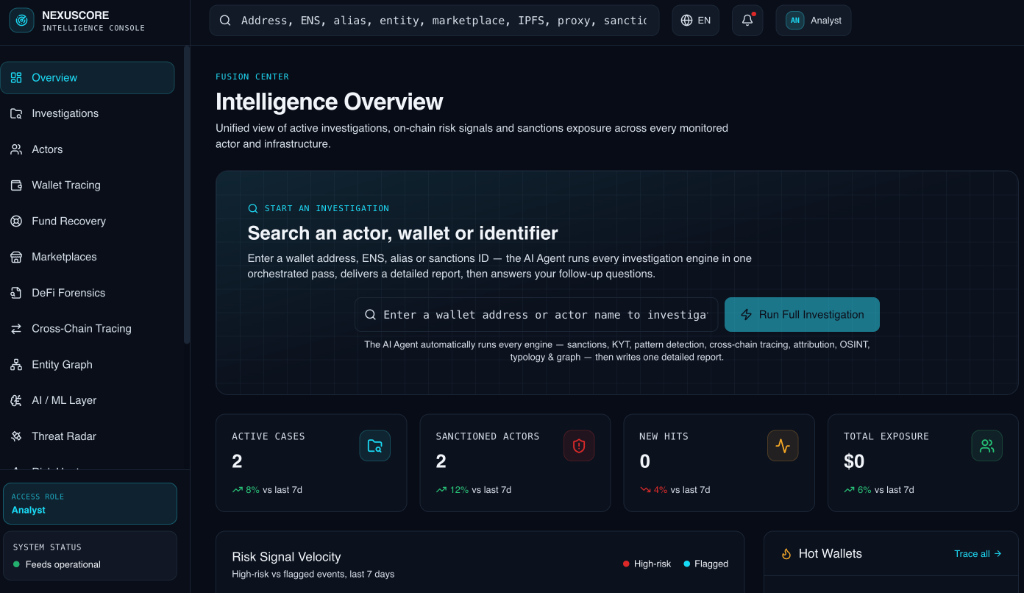
Follow funds across chains, assess risk in real time, and surface sanctions typologies step by step:
Enter a wallet address, ENS, alias or sanctions ID — the AI Agent runs every investigation engine in one orchestrated pass, delivers a detailed report, then answers your follow-up questions.
Coordinate cases end-to-end: link actors, wallets and evidence, and document findings in a shared investigation log.
Unified profiles: linking aliases, wallets, hosting infrastructure, marketplaces, proxies and sanctions typologies into single attributable entities.
This Week's State Actors
Cyberwarfare Watch
Full newsroom
Iranian APT 'Prince of Persia' Deploys US-Based C2 Infrastructure for Global Surveillance Operations
Global Intelligence Alert: Integrity Technology Group Exposed as Front for Chinese State-Sponsored Cyber Operations
Nation-State Actors Deploy 'ARTEX' AI Campaign to Compromise Global Software Supply Chains
China-Aligned Storm-0940 Compromises ConnectWise Cloud Backup via AI-Driven Penetration Framework
Global Intelligence Alert: Integrity Technology Group Exposed as Front for State-Sponsored Cyber Espionage
Global Intelligence Alert: Integrity Technology Exposed as Front for Chinese State-Sponsored Cyber Espionage
Why AI Is Changing Cyber Defense
Artificial intelligence is simultaneously the most powerful tool for cyber defenders and the most dangerous capability enhancement for attackers. AI threat actors can now generate thousands of personalized phishing messages per hour, develop novel malware variants faster than signature databases update, and automate the entire kill chain from reconnaissance to exfiltration. Defensive AI cyber security intelligence is the essential countermeasure.
AI Phishing at Scale
AI generates hyper-personalized phishing targeting specific executives by name, role, and relationships — bypassing both human judgment and automated filters.
Deepfake Executive Fraud
Voice cloning and video deepfake technology enables real-time impersonation of executives for business email compromise and wire fraud.
AI-Enhanced Ransomware
Ransomware groups integrate AI to accelerate network mapping, data identification, and extortion messaging — reducing attack timelines from weeks to hours.
Automated Vulnerability Discovery
AI tools enable threat actors to scan and analyze attack surfaces at speeds previously impossible, finding exploitable vulnerabilities before defenders can patch them.
FARADAY: Anti-Pegasus Spyware Defense 2026
Pegasus and its successors represent the most dangerous class of commercial surveillance tools ever deployed. Operating silently through zero-click vectors, they compromise devices without any user interaction — targeting executives, diplomats, intelligence officers, and high-value individuals across every sector.
Raptor Cyber provides institutional-grade protection programs for governments, corporations, and private organizations seeking to defend their cellular communications, secure their internal networks, and deploy quantum-resistant encryption infrastructure — purpose-built for adversarial environments.
Advanced detection and mitigation of Pegasus and next-generation zero-click spyware targeting iOS and Android devices across organizational fleets.
We architect bespoke, air-gapped communication infrastructures with end-to-end encryption that leaves no metadata footprint — invisible to any surveillance actor.
Post-quantum cryptographic frameworks built to NIST PQC standards, future-proofing your most sensitive communications against quantum-enabled adversaries.
Hardened device configurations and network-level controls that eliminate the attack surface exploited by zero-click delivery mechanisms used by nation-state operators.
NSO Group Pegasus · Predator · Graphite · QuaDream
MONITORED · ANALYZED · NEUTRALIZED
"The Most Sophisticated Encryption Platform in the World"
IMPENETRABLE
OFFLINE · SERVERLESS
KEYLESS · ANONYMOUS
COMMUNICATIONS
"You Cannot Hack, What Isn't There"
Personal. Unique. Individual. Keyless SuperEncryption System for Android, Windows & Mac · Anonymous. Serverless. Offline.
Serverless Private
Communication Network
A serverless, peer-to-peer platform for secure voice/video calls, text messaging, and encrypted file transfers. With advanced encryption and no third-party involvement, it ensures complete privacy while leaving no digital trails.
Supports All Communication Types
Supports secure, high-quality video/audio calls, real-time text messaging, and encrypted file sharing, ensuring seamless and private communication for all needs.
No Data Ever Stored
Completely anonymous with no metadata storage. No need to download any app — it works on every device.
Sophisticated Encryption Algorithms
Encryption keys change randomly every 7 seconds. We generate for every user a personalized encryption algorithm.
Peer to Peer and Full Secrecy
A peer-to-peer communication network that leaves no digital trace online or on the devices used.
Offline Encryption
System
Serverless, air-gapped encryption solution (quantum resistant) designed for full secrecy and unmatched security. Multi-layer encryption, keyless technology, and homomorphic capabilities — ideal for top-classified data storage.
Air-Gapped Communication
Completely disconnected from the internet, ensuring immunity to remote hacking, cyber espionage, and malware attacks. Guarantees maximum security for classified or sensitive data.
Keyless Technology
User-generated encryption keys that are never stored, exchanged, or interceptable. Ensures immunity to digital forensic analysis — keys are not recoverable.
Multi Signature, Multi-Layer Encryption
Multiple layers of symmetric encryption (OTP, AES 256, Blowfish 448, ThreeFish 1024) make data unbreakable and indecipherable, no matter how computational power is applied.
Supports Quantum Resistant Algorithms
Multiple users can encrypt/decrypt files together. Layered access control provides a structured security framework with role-based permissions.
How It Works
1. Keyless — No Key Ever Stored
Encryption keys generated for a few milliseconds and erased permanently — not stored anywhere, never exchanged, immune to interception or hacking.
2. You Are Your Own Manager
Independent offline air-gapped Super Encryption system. No internet, no servers, no third-party. Systems are tailored for each client with dedicated encryption algorithms.
3. Quantum Resistant
Four consecutive layers of symmetric encryption (OTP, AES 256, Blowfish 448, ThreeFish 1024) ensure unbreakable security regardless of computational power.
So If You Are…
ENCRYGMA Is Your Solution!
Strictly Confidential. For Governments, Institutions & High-Profile Individuals.
Who We Serve
Encrygma provides AI cyber security intelligence for organizations across industries and sectors facing sophisticated digital threats.
Enterprises & Corporations
AI cyber security intelligence for corporations facing AI-enhanced phishing, ransomware, supply chain attacks, and espionage.
Financial Institutions
Threat intelligence for banks, investment firms, and payment processors targeted by AI-driven fraud and state-sponsored actors.
Law Firms
Defensive intelligence for law firms handling sensitive M&A, litigation, and regulatory matters facing targeted cyber threats.
Governments & Public Sector
Intelligence for government agencies and public entities facing nation-state cyber operations and critical infrastructure threats.
Critical Infrastructure
Sector-specific threat intelligence for energy, water, telecom, healthcare, transportation, and port operators.
Executives & Family Offices
Personalized cyber risk intelligence for C-suite leaders, board members, investors, and high-net-worth individuals.
8 Intelligence Pillars
Comprehensive AI Cyber Security Intelligence Across Every Threat Domain
Encrygma provides continuous, research-grade AI cyber security intelligence across eight critical threat domains — all defensive, all lawful.
AI Cyber Threat Intelligence
Continuous monitoring of AI-driven attack campaigns, threat actor AI adoption, automated reconnaissance, and emerging AI-based attack techniques.
Mercenary Spyware Intelligence
Defensive awareness of commercial spyware deployments, Pegasus-style attacks, zero-click exploits, and mobile surveillance threats.
State-Sponsored Cyber Attacks
60+ nation-state programs monitored — APT group activity, geopolitical cyber risk, espionage campaigns, and strategic cyber operations.
Ransomware Intelligence
AI-enhanced ransomware trend tracking, group activity monitoring, industry targeting intelligence, and extortion technique awareness.
Executive Cyber Risk
Personalized intelligence for C-suite, boards, investors, and VIPs facing deepfake impersonation, spyware, and targeted cyber threats.
Critical Infrastructure
Sector-specific intelligence for energy, water, telecom, healthcare, and transportation facing OT/ICS-targeted and nation-state threats.
Zero-Day Risk Monitoring
Early exposure awareness, patch prioritization intelligence, exploit-risk scoring, and vendor advisory monitoring.
Cyber Intelligence Reports
Board-level intelligence reports providing actionable insight into AI-driven threats, sector-specific risk, and defensive recommendations.
Request an AI Cyber Security Intelligence Briefing
Enterprises, executives, governments, and critical infrastructure operators can request personalized AI cyber security intelligence briefings tailored to their threat exposure and risk profile.
Our Intelligence Methodology
Encrygma derives all intelligence from publicly available sources, government advisories, peer-reviewed research, security vendor publications, and open-source intelligence analysis. We apply editorial verification standards to assess confidence levels and severity. All intelligence is classified for defensiveness — we never publish attack instructions, exploit code, or operational offensive guidance.
Read our full methodologyFrequently Asked Questions
What is Encrygma?
Encrygma is an AI cyber security intelligence platform providing defensive threat intelligence, cyber risk analysis, ransomware intelligence, spyware defense insights, deepfake threat awareness, and state-sponsored attack reporting for enterprises, executives, and governments.
What is AI cyber security?
AI cyber security covers both the use of AI to detect and respond to cyber threats, and the analysis of how adversaries use AI to conduct more sophisticated attacks including AI-generated phishing, deepfakes, automated reconnaissance, and AI-assisted malware development.
Who does Encrygma serve?
Encrygma serves enterprises, executives, governments, financial institutions, law firms, family offices, and critical infrastructure operators who need continuous AI cyber security intelligence.
Is Encrygma a defensive intelligence platform?
Yes. Encrygma is exclusively a defensive intelligence platform. We do not provide hacking tools, malware, exploit code, unauthorized access instructions, or any offensive cyber capability.
Intelligence Domains
AI Cyber Security Intelligence by Domain
Request an AI Cyber Security Intelligence Briefing
Enterprises, executives, governments, financial institutions, and critical infrastructure operators can request a personalized AI cyber security intelligence briefing tailored to their threat exposure.
Request BriefingGet the Weekly Cyberwarfare Briefing
State cyber operations, AI-powered attack campaigns, and offensive cyber industry developments — delivered to your inbox every week.